

Configure SSL offloading for HAProxy
Last updated: · Applies to Roxy-WI 9.2 and later.
Set up an HTTPS listener with Roxy-WI 9.2 and use the certificate catalog for subsequent certificate changes.
About SSL offloading (TLS termination)
With TLS termination, HAProxy presents the certificate and handles the HTTPS connection from the client. The connection from HAProxy to the backend is configured separately: it can use HTTP or its own TLS connection. Choose that transport explicitly for your application.
Roxy-WI configures the HAProxy listener and manages its certificate material. Uploading a certificate and creating a TLS bind are separate steps.
Prepare the certificate and server
Prepare a PEM containing the certificate chain and its matching private key for the hostname clients will use. Connect the HAProxy server to Roxy-WI, configure SSH and cert_path, and make sure the intended HTTPS port is available.
For a certificate you already have, open HAProxy → SSL, select the server and use Add → Save to disk only. For an ACME-managed certificate, follow the Let's Encrypt draft, staging and issuance workflow. Inspect every HA target before configuring the bind. See certificate upload for the 9.2 dialog and supported file types.
Create and apply an HTTPS listener
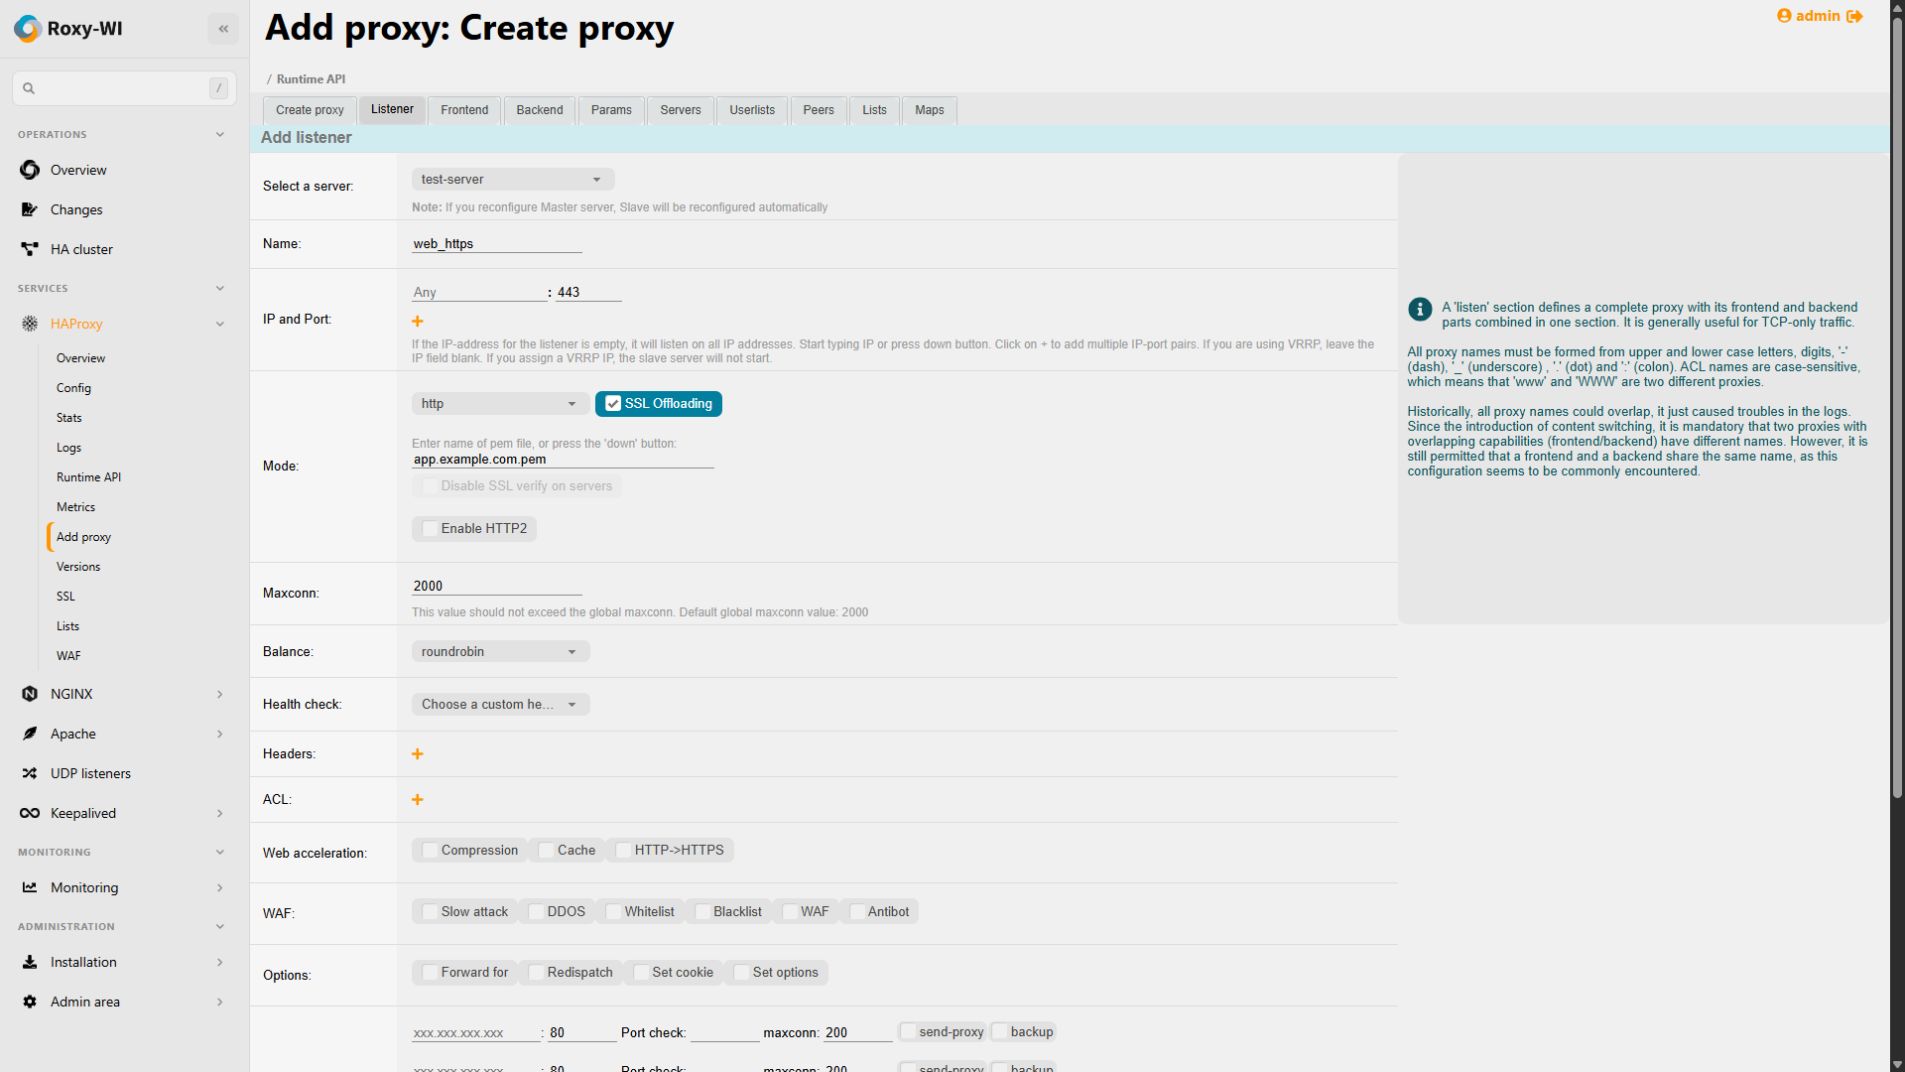
- Open HAProxy → Add proxy and choose Listener or Frontend. Select the server and give the proxy a name.
- Set the bind IP and HTTPS port (normally 443), select http mode and enable SSL Offloading.
- Enter or select the uploaded PEM filename in the certificate field. Configure the backend servers for a Listener, or the backend routing for a Frontend.
- Review the generated configuration and the chosen backend transport. Validate and deploy it using the configuration workflow allowed by your group's policy. Creating or changing a bind requires applying configuration; uploading a file alone does not enable HTTPS.
- Connect with the intended hostname, confirm the certificate names, chain and expiry, and check that requests reach the expected backend. Return to the SSL catalog to inspect In HAProxy and On disk.
Replace certificates after setup
Once the PEM is loaded and its disk state is Matches, use Actions → Update certificate → Save and apply to HAProxy on the SSL page. In 9.2 this persists the replacement and applies it through Runtime API without reloading HAProxy. Follow History and inspect the result on every target.
To add another certificate without changing an existing HTTPS bind, the bind must already load a certificate directory or crt-list. Use Add → Apply immediately to HAProxy without reload and select that source. This option does not create a new bind. Read the requirements and recovery procedure before using it.