

Internal and service logs
Last updated: · Applies to Roxy-WI 9.2 and later.
Choose a log source
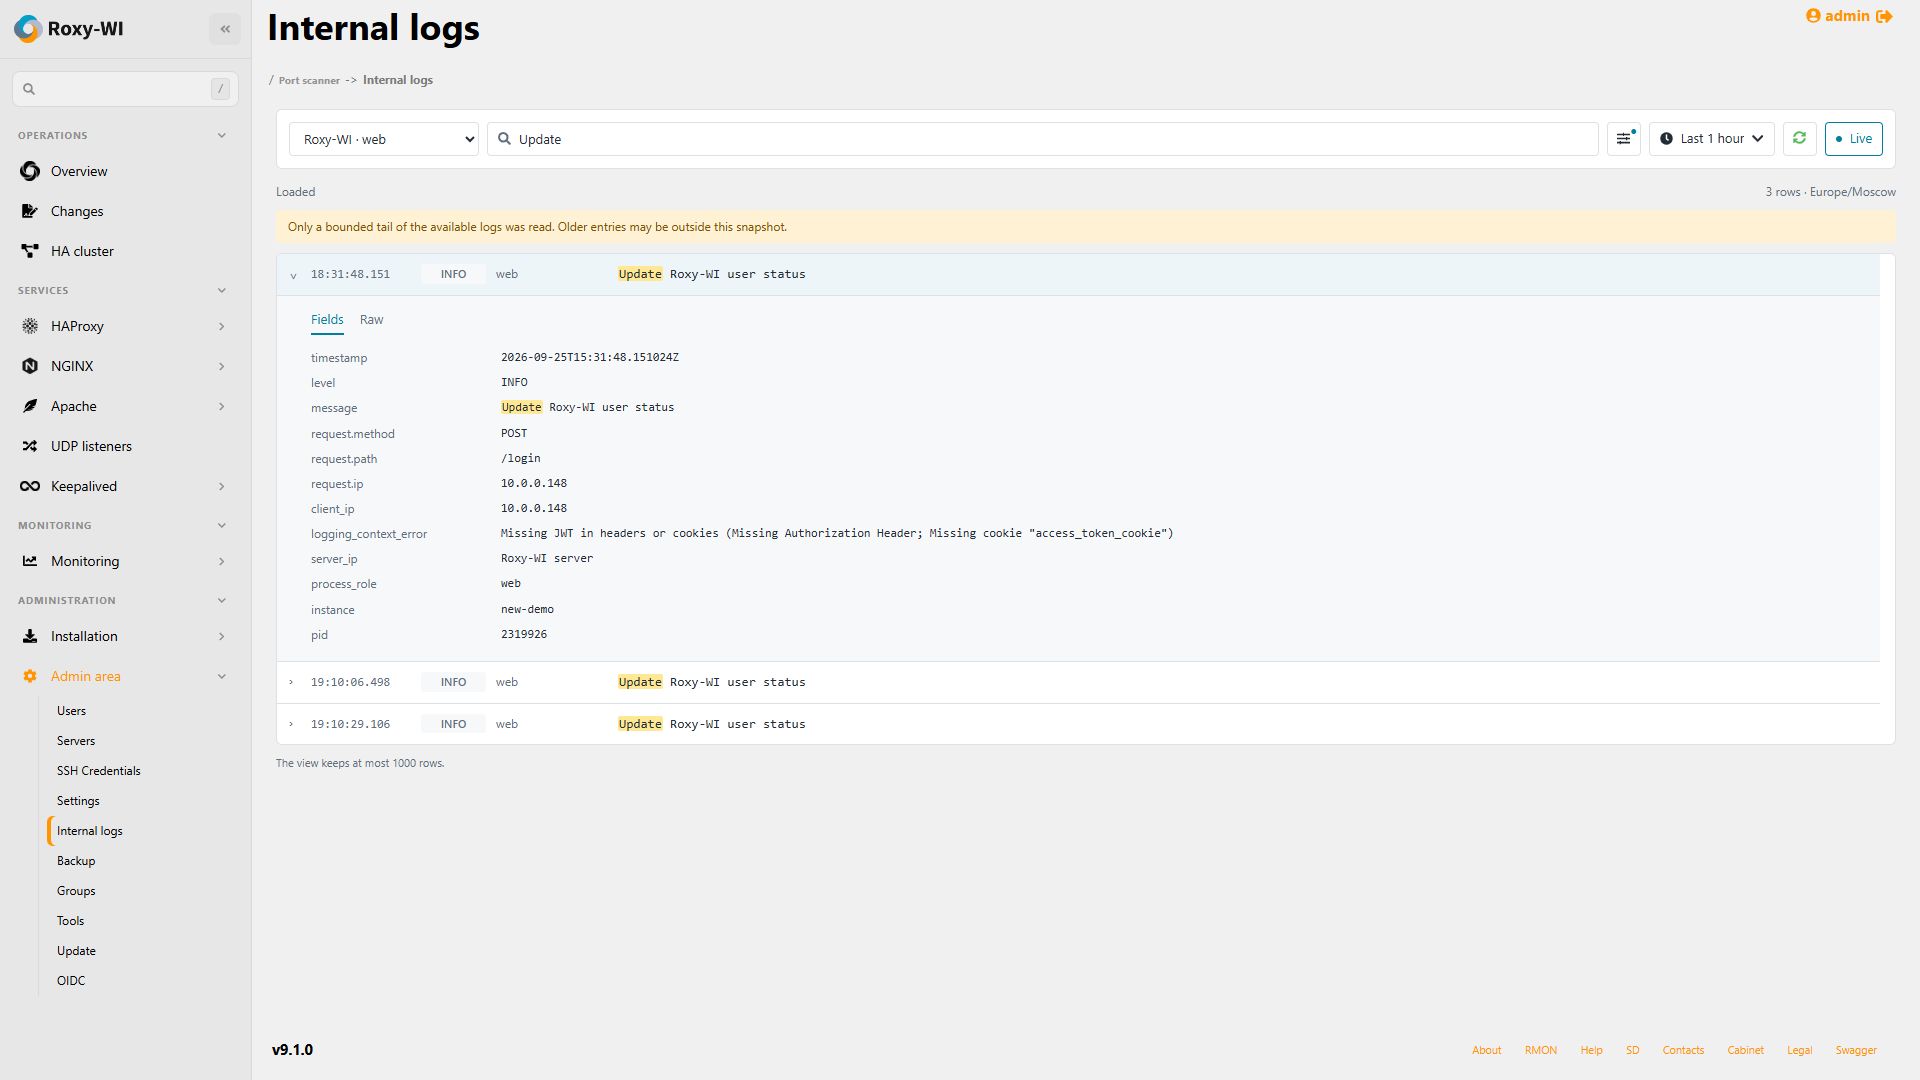
Open Admin area → Internal logs for Roxy-WI events. In installations with the shared journal enabled, select Roxy-WI · all processes or narrow the source to Web, Scheduler, Operations or Service events. Package installations also expose files from their configured log directory; available sources depend on the deployment.
To inspect HAProxy, NGINX, Apache or Keepalived, open that service's Logs page and select a managed server and log file. WAF logs also support the shared viewer. Service logs are read over SSH from the managed host, or its configured syslog server when central syslog is enabled.
Time range and search
- Select a relative interval, from the last five minutes to the last seven days, or set an absolute start and end date/time. Absolute ranges may cross midnight and span up to 31 days.
- Choose browser time or UTC. The choice also determines how service timestamps without an explicit offset are interpreted. Roxy-WI JSON timestamps use UTC.
- Enter literal text in Find and press Enter or Refresh to apply it. Matching text is highlighted in messages and details; matching is case-sensitive.
- Open Additional filters to set Exclude, Rows or Auto-scroll. Exclude also matches literal text.
- Expand a structured row to inspect its fields or original record. Records show time, severity, process and message; plain-text logs remain readable.
Follow logs with Live
Choose a relative time range and click Live to append new records about every two seconds. Pause keeps the read position so Live can resume. Hiding the tab pauses following. Disable Auto-scroll to inspect older records while new entries arrive; opening a record keeps your scroll position.
Service Live requires Python 3 and noninteractive sudo on the log host, with the existing SSH credentials. Each bounded read runs a temporary read-only helper over SSH; no agent is installed and no SSH session remains open while idle. Refresh and absolute ranges use ordinary SSH snapshots.
The service reader starts at the file's tail, then follows its byte position. It detects truncation, follows renamed files and looks for unread records in recent uncompressed rotations. Temporary SSH failures retry with backoff up to 30 seconds. A deleted or compressed rotation may leave a gap, which the viewer reports.
Changing the source or filters starts a new view. Cursors expire after 24 hours; use Refresh to start again. The browser retains at most 1000 rows and removes entries outside the moving relative interval. Live is for inspection; keep the original logs for a complete archive.
WAF events and audit transactions
Open Logs from a HAProxy or NGINX WAF card, then select WAF events or WAF audit. Events use HAProxy's waf.log or NGINX's error.log. Audit uses /var/log/haproxy/waf/audit.log or /var/log/nginx/waf/audit.log on the managed server.
Audit records are displayed as complete ModSecurity transactions, including their multiline sections. Expand a transaction to read it; Find and Exclude search the record. With Live, an unfinished transaction waits for completion rather than appearing as separate lines. The audit reader accepts transactions up to 1 MiB; oversized records are skipped with a notice.
WAF installation configures separate audit files and rotation: daily rotation, a 50 MiB size threshold checked periodically, seven retained rotations, compression and copytruncate. The size threshold is checked by logrotate and is not a hard disk-usage cap. Existing installations must have the matching log configuration; updating Roxy-WI alone does not reinstall remote WAF.
Live follows readable, uncompressed rotations and reports gaps or truncation. The default audit rotation compresses old files; unread records in those compressed files cannot be recovered by Live. Inspect the archived files for a complete history. For missing transactions, check ModSecurity's audit settings, permissions, the selected time range and available files on the managed host. Audit output can contain request data; grant access and set retention accordingly. For application failures, start with events and the WAF status diagnostics.
Structured logs and Overview
Fresh HAProxy and NGINX installations in 9.1 use JSON traffic logs by default, including installations managed through Docker. Existing configurations are preserved. NGINX retains the main access-log format name, including virtual hosts generated by Add; its error logs remain standard text.
HAProxy sends logs to local rsyslog, which writes JSON to access.log, error.log and status.log without a syslog prefix. HTTP and TCP traffic use the format; rsyslog wraps plain-text daemon messages and custom text formats in JSON. Fresh HAProxy log rotation uses delaycompress to leave the newest rotation readable by Live.
The Overview journal shows the latest ten matching entries from the past seven days, newest first, with three initially visible. Expand it to see the rest. Use Refresh to reload recent entries and Show more/Show less to expand or collapse them. The title opens Internal logs, where Find and the other filters are available. With the journal disabled, Overview reads the configured roxy-wi.log.
Storage and access
Containers enable a shared journal alongside JSON stdout. Separate process files live in lib_path/logs, use 5 MiB segments and retain seven days of records. Cleanup runs hourly when records are written. All roles and Web replicas must share the directory and UID.
Set ROXYWI_LOG_STORE_PATH to choose another shared writable directory, or ROXYWI_LOG_STORE_ENABLED=0 to disable the journal. Packages continue using their configured log directory and may opt in to the journal. Container access/error output remains in container logs; local Apache and Fail2Ban choices are package-only.
Group administrators see structured entries tagged with their group ID. Unattributed system/background entries are visible only to the super administrator in the Default group. Each Live request rechecks permissions. Web replicas must share the application secret for signed cursors to work across them.
Missing records and limits
| Symptom | What to check |
|---|---|
| No matching records | Check the source, date range, timezone, Find/Exclude filters and your group access. |
| Service Live fails | Verify SSH access, Python 3 and noninteractive sudo on the actual log host, including a central syslog host when configured. |
| Rotation or truncation notice | Keep enough uncompressed rotations to resume after a pause. Refresh for a new snapshot; inspect the original files for a reported gap. |
| Some lines cannot be parsed | Common JSON, syslog, Apache and NGINX timestamps are supported. Custom formats or continuation lines without timestamps can be excluded with a notice. |
| Older content is outside the snapshot | Narrow the time range or inspect original files/container logs. A time filter does not remove the reader limits. |
Ordinary log snapshots read at most 4 MiB, with up to 128 local files and 256 KiB per local file, and return at most 1000 rows. Ordinary service follow requests read bounded 256 KiB batches; ordinary lines above 64 KiB are skipped with a notice. WAF audit uses its transaction reader with a separate 1 MiB record limit. Use the original files or container logs for older records or a complete export.